Is this with "unix_extensions" enabled or not. Please check timeshift actually works with no error messages in timeshift or permanent timeshift.I can now use the NAS share for timeshift and recordings and both confirmed working.
This is something you'd need to do on the server, as well as the Vix box.Unix extensions are off by default, the line unix extensions = Yes would need adding to /etc/samba/smb-user.conf.
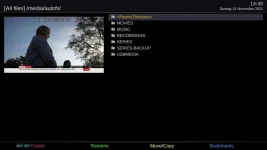
That's correct.Does it only show when it's in use? It only appears in /media/autofs/ when I'm actually using it.
No, it's off by default on ViX, and my Synology Nas makes no reference to it, one way or the other in its configs or gui, so maybe it is on.This is something you'd need to do on the server, as well as the Vix box.
But it is on by default...
unix extensions (G)
This boolean parameter controls whether Samba implements the CIFS UNIX extensions, as defined by HP. These extensions enable Samba to better serve UNIX CIFS clients by supporting features such as symbolic links, hard links, etc... These extensions require a similarly enabled client, and are of no current use to Windows clients.
Note if this parameter is turned on, the wide links parameter will automatically be disabled.
See the parameter allow insecure wide links if you wish to change this coupling between the two parameters.
Default: unix extensions = yes
root@vuultimo4k:/etc/samba/distro# ls -l smb-global.conf
-rw-r--r-- 1 root root 1516 Nov 9 20:37 smb-global.conf
root@vuultimo4k:/etc/samba/distro#
[COLOR="#0000CD"]root@vuultimo4k:/etc/samba/distro# cat smb-global.conf[/COLOR]
[global]
# CVE-1999-0519 and CVE-2000-1200
access based share enum = yes
restrict anonymous = 2
disable netbios = Yes
min protocol = SMB2_02
smb ports = 445
ntlm auth = yes
workgroup = WORKGROUP
security = USER
guest account = nobody
map to guest = Bad User
username map = /etc/samba/private/users.map
min receivefile size = 16384
use sendfile = Yes
aio read size = 16384
aio write behind = true
aio write size = 16384
smb passwd file = /etc/samba/private/smbpasswd
passdb backend = smbpasswd
idmap config * : backend = tdb
obey pam restrictions = Yes
max stat cache size = 64
unix password sync = Yes
pam password change = Yes
server multi channel support = Yes
passwd program = /usr/bin/passwd %u
passwd chat = *Enter\snew\s*\spassword:* %n\n *Retype\snew\s*\spassword:* %n\n *password\supdated\ssuccessfully* .
# Disable printer support for now
disable spoolss = Yes
load printers = No
printcap name = /dev/null
[COLOR="#FF0000"]unix extensions = No[/COLOR]
[COLOR="#FF0000"]allow insecure wide links = Yes[/COLOR]
strict locking = no
oplocks = yes
kernel oplocks = yes
include = /etc/samba/distro/smb-branding.conf
include = /etc/samba/distro/smb-shares.conf
include = /etc/samba/distro/smb-vmc.conf
include = /etc/samba/smb-user.conf
root@vuultimo4k:/etc/samba/distro#
That's correct.
The whole point about automount is that it mounts on request. And unmounts when no longer in use.
Perhaps that should be changed, given that it is needed?No, it's off by default on ViX,...
Perhaps that should be changed, given that it is needed?
Or, if it's felt that the default needs to be off (why?), there should be a menu item to toggle it.
It's (unix extensions) been set to off for at least 4 years, maybe @Willo3092 can try it out? I'm setup differently (nfs) so can't oblige.
What do you need me to do?
unix extensions = Yes
allow insecure wide links = No